The National Institute of Standards and Technology (NIST) has released a roadmap for moving to post-quantum cryptography (PQC), with earlier deadlines for certain sensitive federal
Digital transformation that moves fast and stays secure.
 Bangalore, India
Digital transformation · Enterprise architecture · Security
I lead digital transformation through enterprise architecture and security: cloud, integration, resilience, identity and AI. VP – Enterprise Architect, Coforge.
Explore
01Ideas
Essays on architecture, cloud, security and AI governance
- Your AI budget is a security control
- After a merger, the first security project is a list
- A review gate is a service, not a checkpoint
02Speaking & video
Talks, workshops and interviews

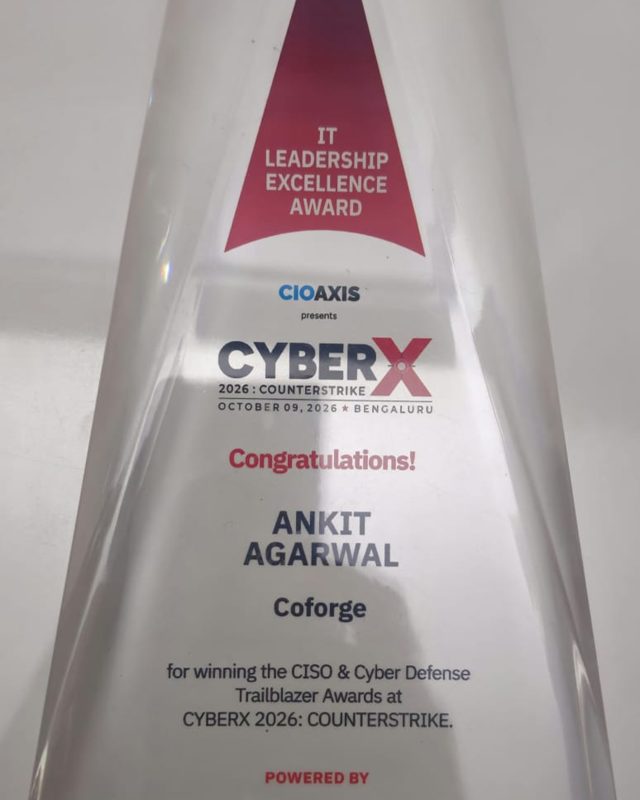
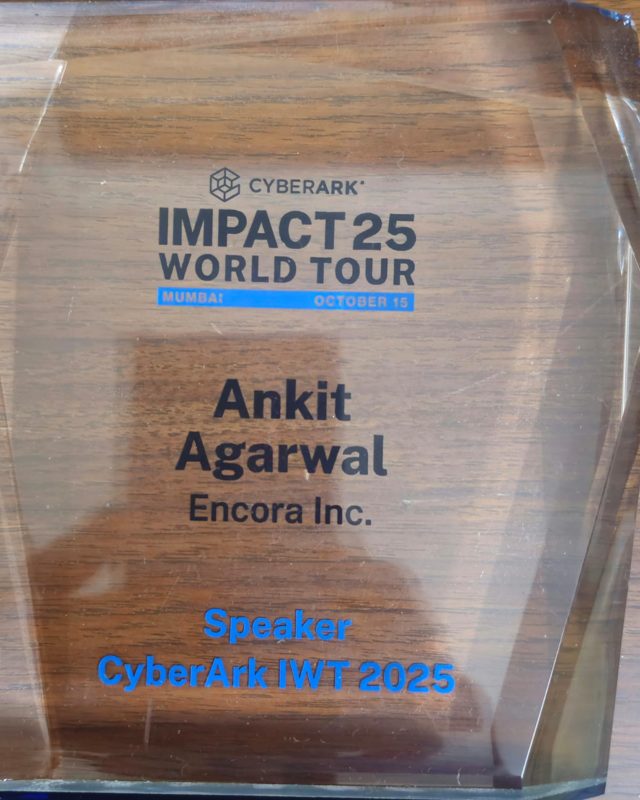
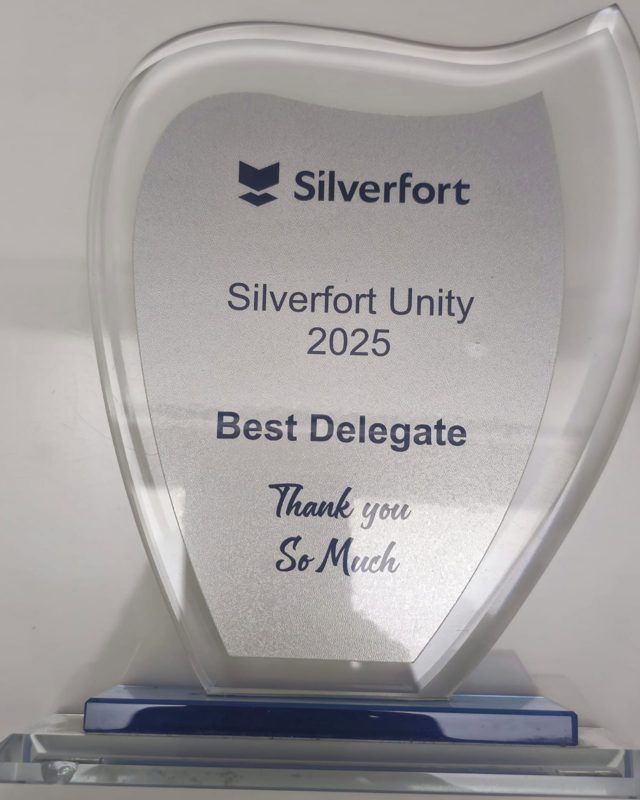
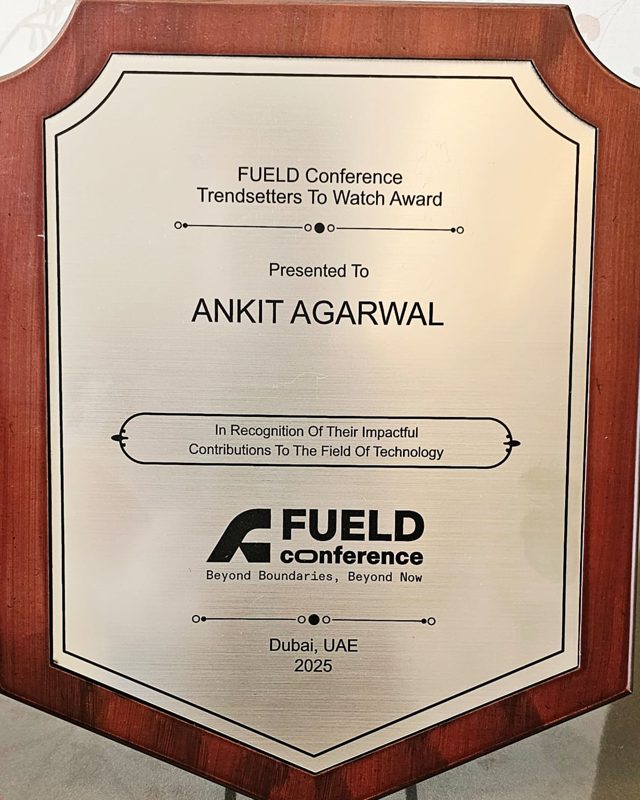
03Recognition
9 awards since 2023
04Work
Architecture, integration, cloud and security programmes
10,000+employees supported3clouds, one platform1M&A integration
See the work →
Cyber Pulse · live
Today in security
Nearly seven in ten people affected by data breaches handled by Kroll were exposed through an outside supplier, according to its Data Breach Outlook 2026. Businesses rely on outsid
The GMO Group has urged customers to disconnect their systems from the internet and shut down computers after a threat actor who breached the company's Onamae Desktop Cloud threate
OpenAI confirmed GPT-6.1 Terra is safer overall than some of its older models, but its safety testing also found other problems. [...]
The University of New Mexico Health Sciences Center disclosed a cyberattack that caused system outages and disrupted patient care and academic activities. [...]
Cyber leaders can get ahead of AI liability with rigorous documentation, transparency, and smart contract negotiations with AI vendors.
A credit card skimming group reportedly compromised a shared analytics script used by e-commerce platform Convertr to steal shoppers' payment data during checkout. [...]
Main bombing sis getting a new look with a wide-scale, ongoing social engineering campaign that might be tied to the Black Basta ransomware gang.
Ukrainian national Artem Stryzhak, 36, had pleaded guilty last year to charges related to participating in at least two well-known ransomware groups.
A recent Shai-Hulud attack shows defenders need real-time visibility into production code and affected services to respond to supply chain compromises.
Latest headlines